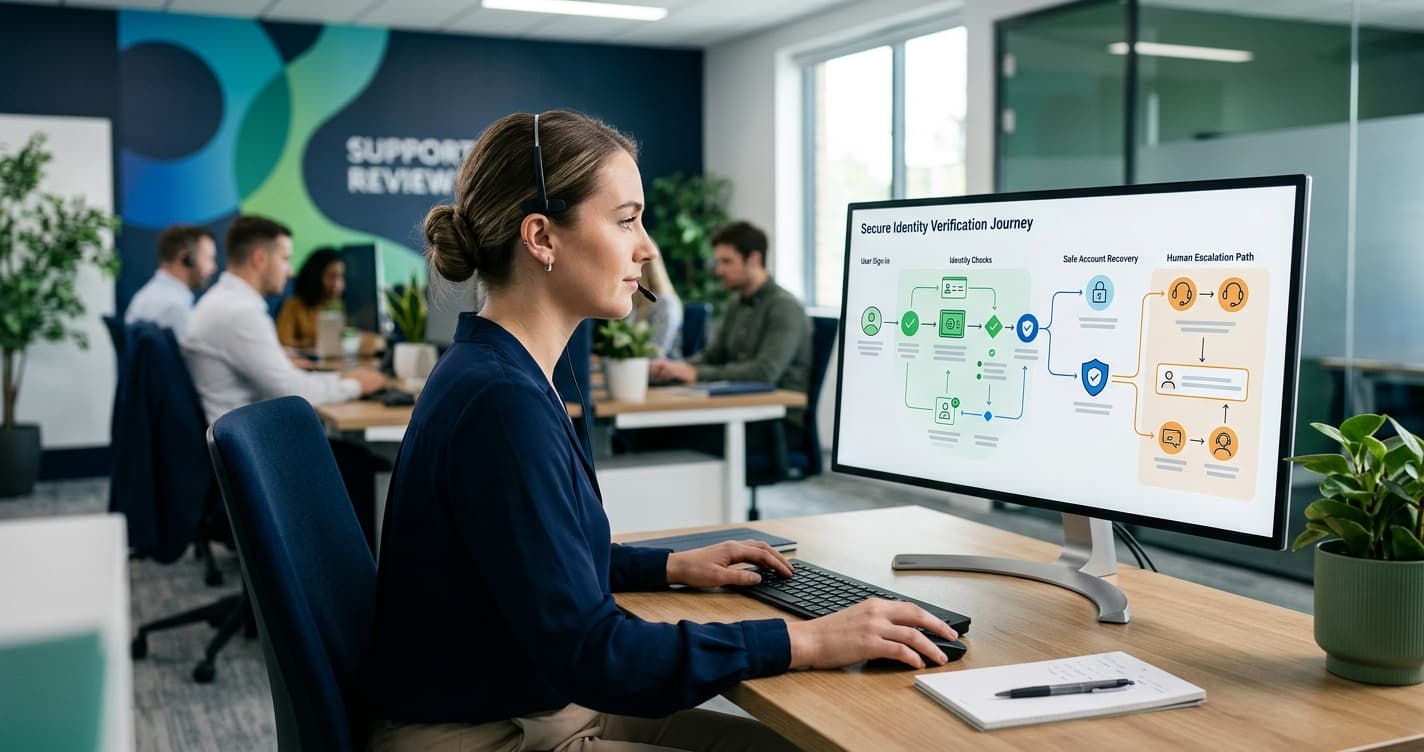
The research question: where does secure verification become avoidable friction?
Identity checks protect customer accounts, but a failed check can also create repeat contacts, abandonment, and unsafe workarounds. This research asks how support teams can measure identity-proofing friction without treating security controls as optional or encouraging agents to bypass them.
The review date for this research is 2026-08-21.
Scope and study method
The evidence scope is a standards review of NIST Digital Identity Guidelines, the W3C Web Content Accessibility Guidelines, the UK National Cyber Security Centre’s authentication guidance, and the FTC’s consumer advice on identity theft. These sources describe assurance, usability, accessibility, authentication, and recovery principles. They do not provide a customer-service failure-rate benchmark.
Study the verification journey as a sequence: request for proof, method offered, attempt, result, fallback, human escalation, and eventual account task. Record the minimum operational fields needed to analyze the journey. Do not store unnecessary identity documents or authentication secrets in a research dataset.
Use a defined observation window and include successful, failed, abandoned, and escalated journeys. For each sampled journey, document the task risk category, offered method, eligibility decision, customer-visible instruction, system result, fallback state, and final safe outcome when known. A second reviewer should check a sample of classifications against the source timeline. Report missing events and unknown outcomes separately from failures. This method makes the evidence scope explicit and reduces the risk that only visible support contacts are treated as the whole population.
Keep the sampling frame stable while the review is under way. Record which channels, methods, and task types were eligible, then note exclusions before comparing outcomes. This prevents a recovery route from appearing more successful simply because abandoned journeys or unsupported devices were left out. Store identifiers that permit reconciliation without copying identity documents or authentication secrets into the research file.
Security and friction are not opposites
NIST’s guidelines connect authentication strength to the risk of the transaction and identity context. A low-risk information request and a high-risk account change should not automatically use the same proofing path. [1] Measuring all failures together can make a strong control look like a poor service or a weak control look efficient.
The NCSC’s guidance on authentication encourages organizations to consider usability and recovery as part of the design. A customer who cannot complete a secure method needs a safe route, not an agent instruction to improvise. [2]
Accessibility is part of the journey. WCAG defines perceivable, operable, understandable, and robust principles for digital content. Support teams should test whether a verification prompt can be completed with the supported devices, input methods, and assistive technologies relevant to the service. [3]
The FTC’s identity-theft guidance is a reminder that exposed personal information can create real consumer harm. A friction study must therefore protect the data it uses and avoid publishing procedural details that would help an attacker. [4]
Analysis should distinguish observation from interpretation. An event log can show that an attempt was rejected or that a customer contacted support again. It cannot, by itself, show whether the customer misunderstood the prompt, lacked access to a device, or encountered a deliberate risk decision. Interview notes, accessibility testing, and approved security review may add context, but each has its own sampling and privacy limits. Keep those evidence types labeled so a staffing decision does not accidentally become a security conclusion.
A friction taxonomy for support operations
Classify the failure before calculating a rate:
| Failure family | Research question | Safe response area |
|---|---|---|
| Comprehension | Did the customer understand the requested step? | Clear instructions and agent explanation |
| Availability | Was the chosen method reachable and functioning? | Channel reliability and fallback |
| Eligibility | Could the customer use the method for this account or device? | Policy and account-state review |
| Accessibility | Could the customer operate the method? | Accessible alternative or assisted route |
| Risk decision | Was the attempt rejected or escalated by a risk control? | Security review, not agent override |
| Recovery | Could the customer safely regain access? | Documented recovery ownership |
The taxonomy is analytical, not a permission list. An agent should not change a risk decision because a customer is frustrated. The purpose is to show whether repeated contacts come from instruction design, system reliability, account state, accessibility, or a deliberate security boundary.
Metrics that preserve the tradeoff
Report verification attempts, successful verification, safe recovery, abandoned journeys, repeat contacts, and confirmed account-task completion. Segment by task risk, method, channel, and customer language or accessibility route when collection is lawful and necessary. Do not publish raw failure rates without denominators and eligibility rules.
Pair service metrics with security outcomes. A reduction in failed checks is not automatically an improvement if it increases unauthorized access. Likewise, a high escalation rate may show a strong control with an inadequate recovery process. The decision is multi-objective.
Use a small case sample to inspect the journey. Compare the system record with the customer-visible instruction and agent notes. Look for loops, contradictory prompts, method changes, and unclear ownership. Red-team the reporting logic by asking whether a case can disappear after a channel switch or case merge.
Boundaries for staffing and agent guidance
Staffing should cover the safe fallback route, especially for high-risk or accessibility-sensitive cases. Training should teach agents to explain the approved path, record the failure family, and escalate according to policy. It should not teach agents to collect more data than necessary or to invent alternative proof.
A support leader can use the taxonomy to ask engineering for a precise fix. “Authentication is frustrating” is less actionable than “customers with a valid account cannot complete the approved method on a defined device path, then return through phone support.” The latter still needs evidence, but it names the journey.
Limitations and conclusion
This review cannot determine the correct assurance level for a specific company or regulated service. Verification failures may be under-recorded when a customer gives up. Security and privacy requirements constrain experimentation. Aggregate metrics can also hide differences between tasks and customer groups.
Identity-proofing friction should be measured as a secure journey with task risk, method availability, accessibility, recovery, repeat contact, and account-task completion in view. CustomerCareStaff teams should optimize for safe completion, not the lowest verification failure rate. A better support record makes it possible to improve clarity and coverage without weakening the control.
That conclusion keeps security ownership with the approved control process while giving customer-care staffing a measurable service improvement path.
Sources
- NIST, Digital Identity Guidelines, identity assurance and authentication concepts.
- UK National Cyber Security Centre, Authentication, authentication and usable security guidance.
- W3C, Web Content Accessibility Guidelines, accessibility principles for digital interactions.
- FTC, Identity Theft, consumer protection and identity-theft risk context.